**How Firewalls Protect Networks From Unwanted Traffic
Every device connected to a network can potentially communicate with other devices, services, and systems. That connectivity makes modern computing possible, but it also creates opportunities for unauthorized traffic to reach systems that should remain protected.
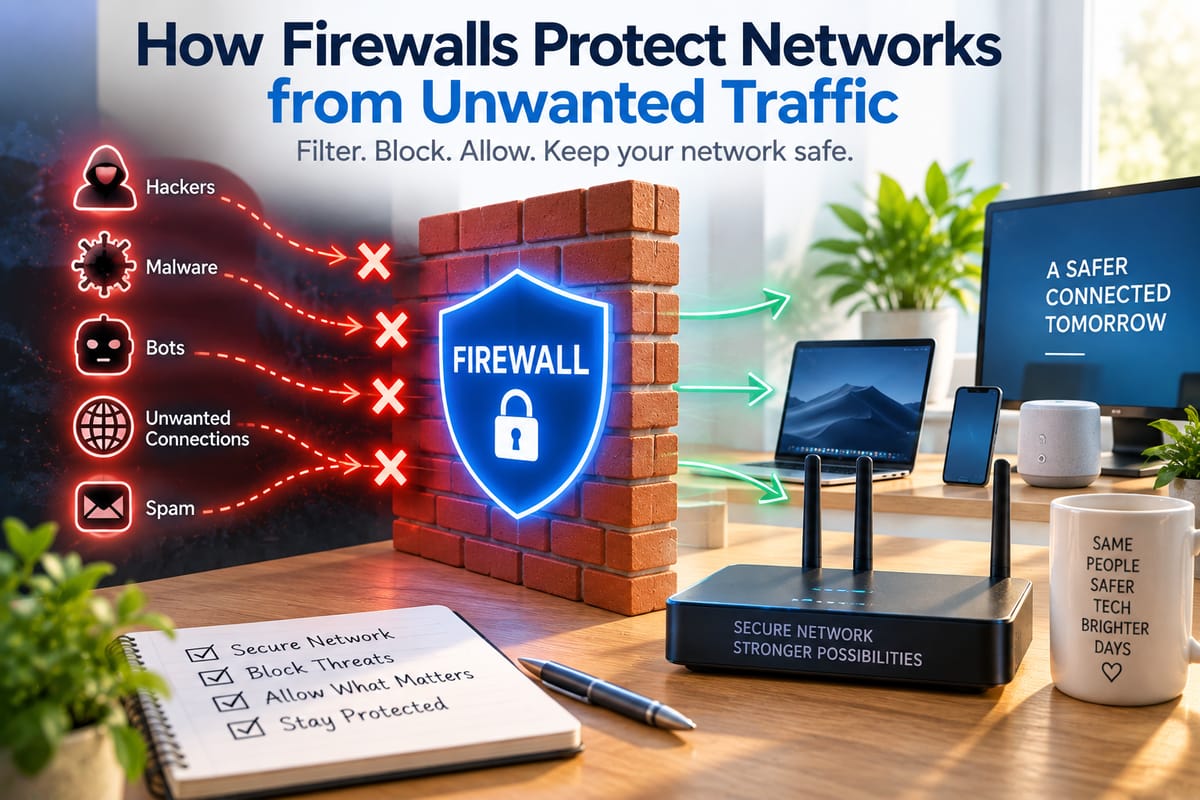
A firewall acts as a security barrier between networks or devices, examining network traffic and applying predefined rules to determine what should be allowed or blocked. It can help prevent unauthorized connections, limit exposure to potentially harmful traffic, and provide administrators with greater control over how systems communicate.
Firewalls are not a complete cybersecurity solution, but they remain an important layer of protection for homes, businesses, data centers, and cloud environments.
What Is a Firewall?
A firewall is a security system designed to control network traffic according to defined rules.
It can sit between a trusted internal network and a less trusted external network, such as the public internet. Firewalls can also be installed directly on individual computers or servers.
Depending on its design, a firewall can inspect information such as:
- Source and destination addresses
- Network ports
- Communication protocols
- Connection state
- Application characteristics
- Traffic direction
- Specific security rules
When traffic matches an allowed rule, the firewall can permit it to continue. When traffic violates a blocking rule, the firewall can reject or drop it.
This basic filtering process helps reduce unnecessary exposure.
Why Networks Need Traffic Control
Without traffic controls, network-connected systems may have more opportunities to communicate than necessary.
For example, a server might only need to accept connections from a specific application, while a business workstation may need access to the internet but should not accept unsolicited connections from outside the organization.
Allowing every type of traffic would create unnecessary exposure.
A firewall provides a way to establish boundaries. Instead of treating all network communication equally, it can apply different rules to different types of traffic.
This principle is an important part of the broader Complete Guide to Network Security.
How a Firewall Decides What to Allow
Firewalls use rules to determine how traffic should be handled.
A rule might specify that traffic from a particular source is allowed to reach a particular destination through a particular port. Another rule could block traffic associated with a specific address, service, or connection type.
For example, a firewall could be configured to:
- Allow web traffic needed by employees
- Permit authorized remote administration
- Block unsolicited inbound connections
- Restrict access to sensitive servers
- Prevent certain devices from communicating with particular networks
- Allow only approved applications to communicate externally
The exact capabilities depend on the firewall technology and its configuration.
Inbound and Outbound Traffic
Firewalls can control both incoming and outgoing traffic.
Inbound traffic originates outside a protected network and attempts to reach an internal device or service. Blocking unnecessary inbound connections can reduce opportunities for unauthorized access.
Outbound traffic originates inside the network and travels toward another network or internet service. Controlling outbound traffic can help prevent unauthorized applications from communicating externally and can limit certain forms of malicious activity.
Monitoring both directions provides a more comprehensive approach than focusing exclusively on incoming connections.
Packet Filtering
One of the fundamental firewall techniques is packet filtering.
Network communications are divided into packets, and a firewall can inspect information contained in those packets. Traditional packet-filtering rules can examine characteristics such as source address, destination address, protocol, and port.
For example, a firewall could allow traffic destined for a particular web service while blocking traffic aimed at an unused port.
Packet filtering can be efficient because the firewall does not necessarily need to inspect the entire contents of every communication.
However, simple packet filtering has limitations. Modern threats can involve application behavior and communication patterns that cannot be understood through basic address and port information alone.
Stateful Inspection
Stateful firewalls keep track of active network connections.
Instead of evaluating every packet as an entirely independent event, the firewall can understand whether a packet belongs to an established connection.
For example, when a device initiates a legitimate connection to an external service, the firewall can track that connection and recognize subsequent traffic associated with it.
This provides more context than basic stateless filtering and can help prevent certain unsolicited packets from being accepted.
Application-Level Filtering
More advanced firewalls can inspect traffic at the application level.
Application-aware filtering can provide greater visibility into how network services are being used. Depending on the firewall, administrators may be able to create rules based on applications, users, web services, or other characteristics.
This can be useful in business environments where simply allowing or blocking a network port is not enough.
Application-level controls can help organizations enforce more specific policies about which services are permitted.
Firewalls Can Block Unauthorized Ports
Network ports provide communication endpoints for different services.
A computer does not necessarily need every possible port to be accessible. Keeping unnecessary ports closed can reduce the number of services exposed to other systems.
A firewall can help enforce this principle by allowing access only to ports required for legitimate operations.
For example, a server hosting a web application may need to accept web traffic while restricting access to administrative services.
Reducing unnecessary exposure is often described as part of a least-privilege approach to network security.
Firewalls and Home Wi-Fi Networks
Firewalls are not limited to corporate networks.
Many home routers include firewall capabilities that help protect devices connected to the household network from unsolicited internet traffic.
This is especially relevant because modern homes may contain computers, smartphones, smart televisions, security cameras, speakers, appliances, and other connected devices.
The security of the wireless network itself is also important. Strong authentication and appropriate encryption help prevent unauthorized users from joining the network, while firewall controls can regulate traffic moving between the local network and external systems.
For more information about protecting wireless networks, see Wi-Fi Security Explained.
Hardware and Software Firewalls
Firewalls can be implemented in several ways.
A hardware firewall is typically a dedicated network device or a firewall function integrated into networking equipment. It can protect multiple devices at once by controlling traffic as it enters or leaves a network.
A software firewall runs on an individual computer, server, or other device. It can apply rules specifically to that system.
Many organizations use both network-level and host-level protections because they provide security at different points.
A network firewall can control traffic entering a segment, while a host firewall can provide additional protection around an individual system.
Firewalls and Network Segmentation
A firewall can also help divide a larger network into separate security zones.
For example, a business might separate:
- Employee workstations
- Servers
- Guest devices
- Security systems
- Financial systems
- Development environments
Rules can then control which zones are allowed to communicate.
Network segmentation can limit the spread of an intrusion. If an attacker gains access to one part of a network, properly configured boundaries can make it more difficult to reach systems in other areas.
Segmentation is particularly useful for organizations that need to protect sensitive systems from less trusted devices.
Firewalls in Cloud Environments
Cloud computing has changed where networks and applications operate, but traffic filtering remains important.
Cloud platforms commonly provide security controls that can restrict network communication between virtual machines, services, applications, and external networks.
Administrators can define rules specifying which systems should communicate and which connections should be blocked.
Cloud firewalls may therefore form part of a broader architecture involving identity management, application security, encryption, monitoring, and access controls.
Firewalls and Encryption Work Together
A firewall controls network communication, while encryption protects information by transforming it into a form that unauthorized parties should not be able to understand without the necessary key.
These technologies address different security problems.
A firewall might prevent an unauthorized connection from reaching a server. Encryption can help protect information if legitimate network traffic is intercepted or accessed improperly.
The relationship between these technologies is explored further in the Complete Guide to Encryption and Cryptography.
Using both can provide multiple layers of protection.
Firewalls Cannot Stop Every Threat
A firewall is an important security control, but it should not be treated as a complete defense.
If an attacker obtains valid login credentials, for example, network traffic may appear legitimate. Similarly, a user can intentionally or accidentally install malicious software that communicates through an allowed connection.
Firewalls may also struggle to identify threats hidden inside legitimate-looking traffic without additional inspection capabilities.
This is why effective cybersecurity generally combines multiple controls rather than depending on a single technology.
Firewall Rules Need Regular Maintenance
A firewall is only as effective as its configuration.
Over time, organizations may add temporary rules for testing, introduce new applications, change network infrastructure, or give employees new access requirements.
If old rules are never removed, the firewall can gradually accumulate unnecessary permissions.
Regular reviews can help identify:
- Unused rules
- Overly broad permissions
- Unexpected open ports
- Temporary exceptions that are no longer needed
- Conflicting rules
- Unauthorized configuration changes
Keeping rules organized makes them easier to understand and maintain.
Logging Helps Identify Suspicious Activity
Many firewalls can record information about network traffic and blocked connections.
Logs can help administrators understand what is happening on a network and investigate unusual activity.
For example, repeated attempts to reach a closed service could indicate scanning or other suspicious behavior. Unexpected outbound connections from a workstation may also deserve investigation.
Firewall logs are most useful when they are reviewed alongside other security information rather than treated as an isolated source of evidence.
Firewall Configuration Requires Balance
Blocking everything may appear to provide maximum security, but it can also prevent legitimate systems from functioning.
On the other hand, allowing too much traffic can undermine the purpose of the firewall.
Effective configuration therefore involves balancing security requirements with legitimate business or personal needs.
A good rule generally allows necessary communication while restricting everything that does not have a legitimate purpose.
This approach can reduce unnecessary exposure without making normal operations unnecessarily difficult.
Firewalls and Data Protection
Network traffic controls are closely connected to data protection because many security incidents involve unauthorized attempts to access or transmit information.
A firewall can help establish boundaries around systems that store sensitive information, but additional safeguards are necessary.
Access controls, authentication, encryption, secure backups, endpoint protection, software updates, and appropriate user practices all contribute to protecting digital information.
For a broader overview, see What Is Data Security and How Can Digital Information Be Protected?.
A Layered Approach Provides Broader Protection
Modern cybersecurity relies on defense in depth.
A typical environment may combine:
- Firewalls to control network traffic.
- Authentication to verify users and devices.
- Encryption to protect information.
- Endpoint security to monitor individual devices.
- Network segmentation to limit unnecessary communication.
- Security monitoring to identify unusual activity.
- Software updates to address known vulnerabilities.
- Backups to support recovery after data loss or disruptive attacks.
- User awareness to reduce risks associated with social engineering and unsafe behavior.
Each layer addresses different weaknesses.
If one control fails, another may still prevent or limit the consequences.
Making Firewalls Part of a Stronger Security Strategy
Firewalls provide a fundamental method for controlling who and what can communicate across network boundaries. By examining traffic and enforcing rules, they can block unnecessary connections, restrict access to sensitive systems, and reduce the network's exposure to unwanted activity.
Their role has also expanded beyond simple traffic filtering. Modern firewall technologies can support application awareness, network segmentation, monitoring, cloud security, and more sophisticated traffic controls.
Still, a firewall should be viewed as one component of a larger cybersecurity strategy. Strong authentication, secure Wi-Fi, encryption, updated software, careful configuration, monitoring, and data protection practices all work together to create a more resilient environment.
When properly configured and regularly maintained, firewalls provide an important line of defense between trusted systems and the unwanted network traffic constantly moving through today's connected world.